Signing keys
Each AIGW ResourceResourceThe downstream system registered in a Project. Its kind (Token exchange or OAuth client) decides the role AIGW plays. has signing keysSigning keyA per-Resource ES256 key AIGW uses to sign assertions sent to the merchant authorization server, published at the Resource JWKS URL. used for merchant-facing JWT assertions and client authentication. The ConsoleAIGW ConsoleThe AIGW developer dashboard (DevCon) where you manage Accounts, Projects, Resources, agents, and policies. describes them as the keys used to verify the Resource's token-exchange JWTs.
Key format
AIGW uses:
- EC P-256 keys;
- ES256 signatures;
kidvalues in theapp:<id>/jwtstyle;- a per-resource JWKSJWKSJSON Web Key Set: a published set of public keys used to verify JWT signatures. endpoint:
https://api.aigw.eval.loginid.ai/<RESOURCE_ID>/.well-known/jwks.json
A first signing key is generated automatically when the Resource is created, so the JWKS URL is usable immediately.
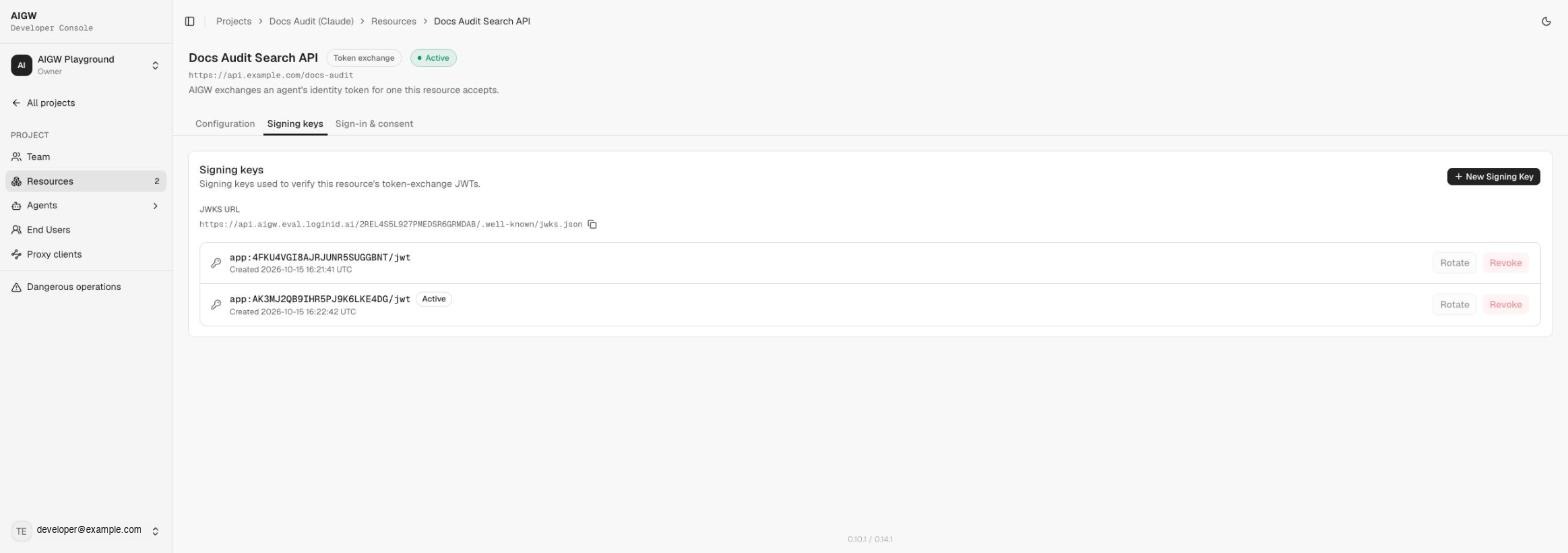
Managing keys
Open Resource → Signing keys. The page shows the JWKS URL (with a copy button) and every key with its kid, creation time, and an Active badge on the current key.
| Action | Effect |
|---|---|
| New Signing Key | Creates a new key and makes it Active. Older keys stay in the JWKS. |
| Rotate | Rotates a key. |
| Revoke | Revokes a key so it is no longer trusted. Revoke an old key only after verifiers no longer need it. |
Rotation
Creating a new signing key makes the new key active while older keys remain present in the JWKS, allowing verifiers to continue validating tokens/assertions signed with previous keys during rotation. For example, after New Signing Key, the Resource JWKS returned both the original and the new ES256 key.
Merchant authorization servers should consume the JWKS URL rather than pinning a single raw public key when their platform supports it.
Two AIGW key sets
Resource signing keys are not the core AIGW JWKS used for agent-facing AIGW tokens. There are two issuer/key contexts:
- core issuerCore issuerThe shared AIGW authorization server that issues agent-facing access tokens and hosts the token endpoint./JWKS for AIGW access tokensAIGW access tokenThe token an agent receives after the user authorizes it. It says which user approved which agent for which scopes.;
- per-resource issuerPer-resource issuerThe AIGW authorization server dedicated to one Resource, at /<RESOURCE_ID> on the AIGW API host. Agents discover it; merchants trust it./JWKS for JWTs AIGW presents to the merchant AS.
See JWTs and JWKS.